Default passwords on office printers expose sensitive data to hackers
An audit of agency machines reveals that standard settings on multifunction devices can store documents and network keys, creating entry points for cyber intruders.
By Noor Graham ·
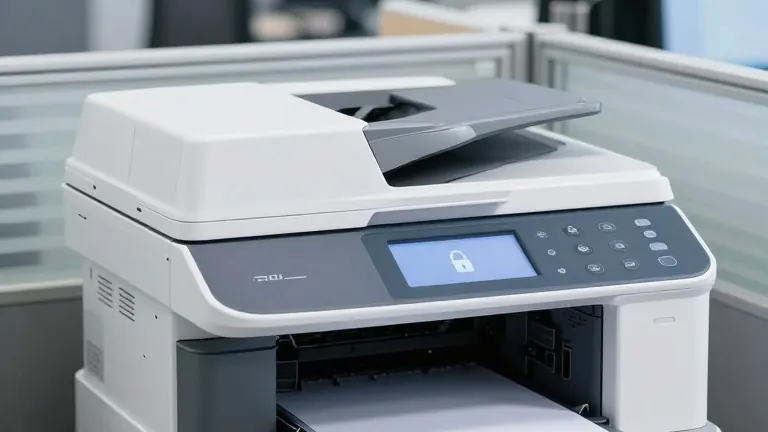
Ordinary office workers face a new digital threat from the machines sitting in their breakrooms. A confidential audit of several government agencies found that outdated printer settings allow hackers to access sensitive information. The devices often store more than just printed pages, holding scan histories, address books, and network configuration files.
The audit identified specific vulnerabilities in modern multifunction devices. Many units contain hard drives and firmware that run on default passwords set by the manufacturer. If administrators never change these initial login credentials, external attackers can plug into the network and pull data directly from the machine. This risk affects entities ranging from hospital records departments to school administration offices.
The findings come from InvestigateTV+ after the team received a detailed report on the security posture of various agency machines. The devices described are standard office equipment used for daily tasks like copying and scanning. Because these printers connect to internal networks to share files, a compromised unit acts as a bridge to the rest of the organization's data systems.
Sarah Magruder Lyle, president and CEO of Common Ground Alliance, noted that similar blind spots exist in physical infrastructure. She warned, “You can’t assume you know what’s underground. You have to assume that you don’t,” a principle that applies equally to digital infrastructure where users rarely check the default state of their hardware.
The report details how these machines operate behind the scenes. While users see a simple control panel, the device processes data continuously. It retains logs of every document scanned and keeps a record of every email address used in the device's history. When these files sit on an unsecured network with open default credentials, they become accessible to anyone who finds the device's IP address.
Alcor, a nonprofit in Arizona, operates on a similar philosophy of preparing for future needs, though their focus is biological preservation. Since the 1970s, the organization has used subfreezing temperatures to pause the dying process. Their work highlights the gap between current technology and future capabilities, a gap that printer manufacturers have left open for years by not updating default security protocols.
In the New Orleans metro area, the band Vet Jams is using live country music to address mental health stigma among veterans. The group combines performances at local bars with open conversations about therapy. This approach mirrors the need for clear, direct communication in other sectors, such as the tech industry, where complex security settings require simple explanations for users to maintain safe defaults.